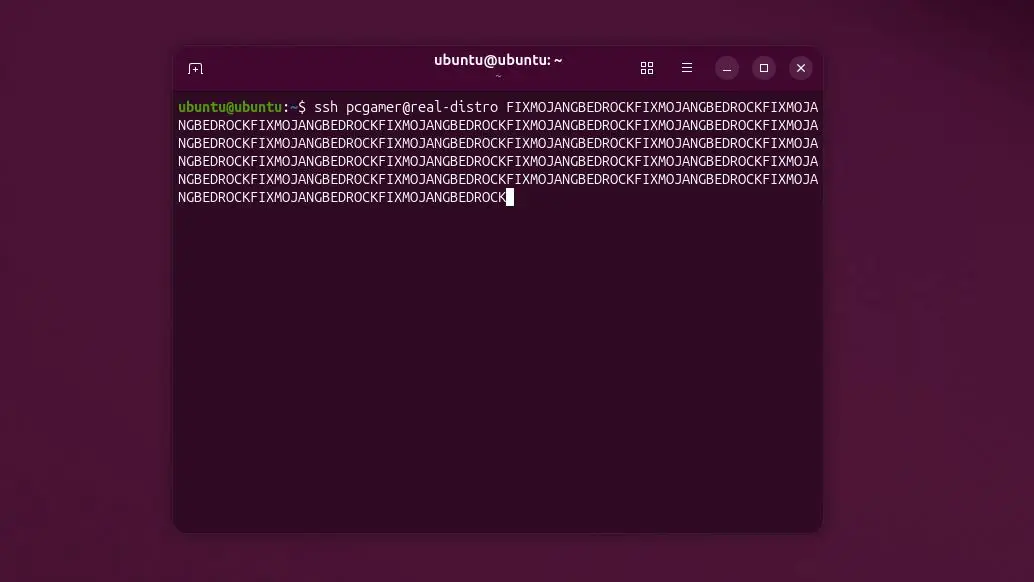
Some implementations of secure shell (SSH), one of Linux's most trusted and secure connection protocols, have been found vulnerable to the most peculiarly simple methods of bypass: spamming characters.
On some distros, simply type 257–1,024 characters and you get access to the root (admin) login. Thankfully, the list of vulnerable distros is quite small and niche, and OpenSSH has already issued a workaround/fix.